Little Snitch 6.5 (macOS)
One download for Apple Silicon and Intel. Opens the install steps and mirrors.
- Version
- 6.5
- Size
- 39 MB
- Earliest macOS
- 14 or later
- CPU type
- Universal
- Updated
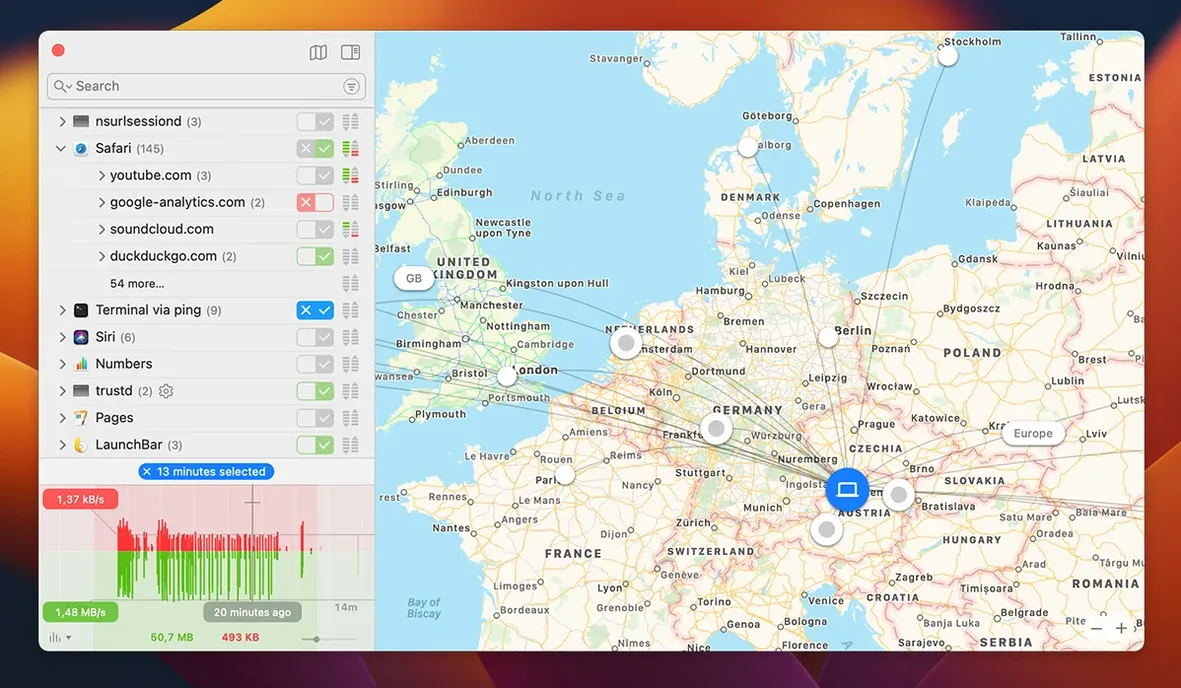
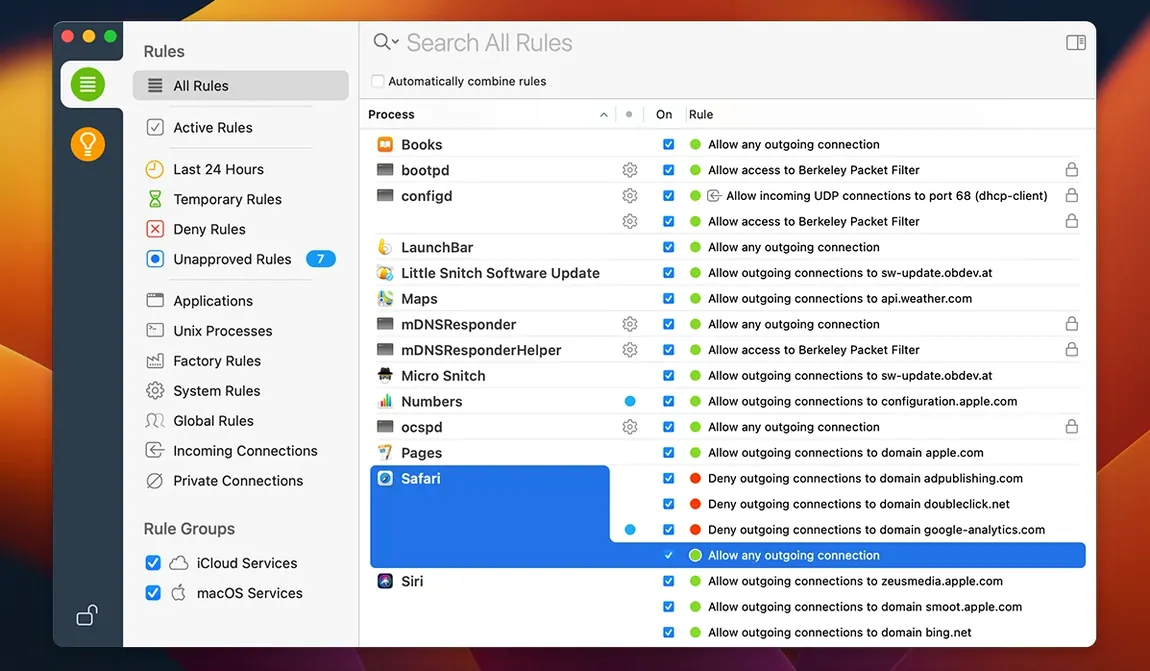
Little Snitch is an application firewall that lets you approve or deny every Mac network connection before it leaves the machine.
An experienced user quickly moves past the basic allow/deny pop-ups and into the parts that save real time.
1. Build a base with Silent Mode
Switch to Silent Mode from the status bar icon. It defers all connection alerts. Spend an hour running your usual apps, then open Rules and sort the pending decisions in bulk. A single pass approves known services and blocks telemetry you never agreed to.
2. Pull data from the command line
The included little-snitch CLI tool reads rules, dumps traffic stats and checks the firewall state. Pipe a JSON export into your own scripts for overnight audits or deployment checks across the school lab.
3. Track what changed with bundle integrity
Version 6.5 monitors app bundle integrity while running. If an app is modified on disk after you granted a rule, the rule suspends. You catch compromised binaries without watching the monitor all day.
4. Read encrypted DNS in the monitor
Improved DNS handling in 6.5 decodes more encrypted queries inside the Network Monitor. You see which domains are looked up even when the resolver uses DoH or DoT.
The NAT64 implementation is still experimental, but it already translates IPv4 addresses inside a CLAT environment cleanly. If your network testing involves single-stack IPv6, the toggle is in the advanced settings.
Drop the timeout to 20 seconds
Out of the box, the alert frequency can overwhelm anyone. Two changes settle things down quickly.
Drop the confirmation timeout from 60 seconds to 30, maybe 20. A shorter window forces decisions faster. Less pile-up in the queue.
Turn off the connection alert sound. The default pop is loud and nobody needs a beep every time Mail checks the server. The visual banner is enough.
Enable the menu bar connection counter. It shows active connections at a glance, a quicker check than opening the full monitor. You spot a runaway process before it saturates a link.
Set Research Assistant to "Check for known services only". The fuller lookup adds a delay on every alert while it phones home. The basic check still identifies common Apple and Adobe endpoints, and it keeps alerts snappy.
It touches mDNSResponder too
Little Snitch sits between every app and the network stack. That means it touches anything that opens a socket: browsers, updaters, background daemons, even the system's own mDNSResponder.
The Network Extension filter runs in user space, not as a kernel extension. The older kext approach is gone. On Apple Silicon this matters because the filter loads without reducing the system security policy. No need to dial down SIP or boot into recovery.
The software needs Full Disk Access to read the rules file and write new ones. Without it, rules won't persist across reboots. The installer prompts for this; skip it and you get a firewall that forgets.
The world map view pushes that slightly higher because it resolves IP addresses to coordinates, but the memory releases once you switch to the plain server list.
Compatibility covers macOS 14 and newer, including the seed builds of macOS 27 Golden Gate. Intel and Apple Silicon machines get the same binary, the same filter engine. No feature gap between architectures.
Beware permanent allow from impatience
The biggest one: allowing any connection in the first alert because the prompt gets in the way. That grants a permanent rule to a domain you haven't checked. Five minutes later the app phones a tracking endpoint and you never see it.
Related mistake: setting the rule scope to "Any server" instead of limiting it to the specific domain in the alert. A rule for *.api.service.com is safer than an open door to the whole internet. Beginners often widen the scope to stop repeat alerts, then forget they left a gap.
Another common slip is stacking temporary rules instead of building a permanent base. Build the permanent rules first, then use temporary rules for one-off tools.
Quiet Mode confuses people who think it blocks everything. It doesn't block. It postpones decisions. Connections that match no existing rule proceed silently, and the decision sits in the backlog. If you want a block-all posture, you build a rule that denies everything and then punch holes for known services. Quiet Mode is the wrong tool for that job.
Beginners also miss that the Network Monitor shows connections in real time but doesn't log them indefinitely. The hourly traffic history gives totals, not a full packet log. If you need a forensic record of every DNS query and TCP handshake, export the data via the CLI or pair Little Snitch with a separate logging tool.
- macOS 27 Golden Gate support added
- App bundle integrity monitoring while running
- Experimental NAT64 implementation (RFC 6052)
- Encrypted DNS handling improved
- macOS 14 or later
- Intel or Apple Silicon Mac
- Languages: English, German
Staffroom comments 0
Sign in or create an account here to leave a comment.
Nobody has commented on this one yet.
Other Utilities tools
All Utilities tools-
 LanScan
8.2.17
17 MB
Utilities
-
 MediaMate
3.8.4
7 MB
Utilities
-
 iTubeGo
10.15.0Intel Macs only
115 MB
Utilities
-
 iMazing
3.6.5
242 MB
Utilities
-
 iExplorer
4.6.0Intel Macs only
30 MB
Utilities
-
 iDownerGo
10.15.0Intel Macs only
76 MB
Utilities
-
 Mountain Duck
5.3.2
187 MB
Utilities
-
 MouseBoost Pro
5.3.0
17 MB
Utilities